
 06Oct
Data protection for companies
Secure Cage Systems protect your computing equipment
This article is about the security of IT and server systems in companies. Many entrepreneurs think of data protection in terms of external attacks on the software, for example by hackers. Or of misuse such as data theft via USB stick or manipulation of the database by the company's own personnel. The software-based perspective is obvious when it comes to considering existential risks. If IT no longer functions, there is a threat of collapse. There is also a physical component that plays a role in risk assessment.
Computer systems are often not adequately protected
Too often, server facilities are not protected at all or are inadequately protected and accessible to anyone. Where there happens to be space, in the copy room, in the storage room or where the noise of the processors does not disturb the employees. Shared space with business or residential parties also increases the risk of unauthorized access and entry.
Objective risk assessment required
At SCS - FACO, we produce security cages to protect server equipment from theft, tampering and damage. Therefore, we know that in many companies physical data protection has not yet been integrated into a security concept, or not sufficiently so. We wonder why physical data security is still given low priority in many companies. After all, the damage that a stolen or damaged server represents for the company is just as existential as a hacker attack on the software.
Our conclusion is that this danger is subjectively not considered likely. An objective assessment is therefore urgently needed. The legislator provides guidelines for this.
Physical data protection by law
Based on:
- DSGVO (Basic Data Protection Regulation) Art. 32 Para. 1 lit. a-d
- BDSG (Federal Data Protection Act) § 64 para. 3 p.1
- GoB (principles of proper accounting)
Essentially, it is a matter of ensuring the functionality of the systems and setting up local access authorizations. It must therefore be regulated who may have access to the computer systems - keyword "access control". Precise information on this can be found in the "Technical Organizational Measures", or TOMs for short:
- Fences, gates and other spatial limitations.
- Security locks
- Locking systems with code locks
- Chip cards for locked areas
- Access barriers secured with biometric features
These areas are covered by our Security Cages in a DSGVO-compliant manner.
Ensuring security with Secure Cages
We design our Secure Cages according to the respective local conditions. The individual setup can be implemented in just a few weeks. The costs are low over the lifetime of the cage. For more information and concrete product examples with prices, please visit our Secure Cage Systems website.
In addition to physical protection, Secure Cages are a strong symbol of responsible handling of personnel and customer data, both externally and internally, and have a positive effect on the corporate image.
More
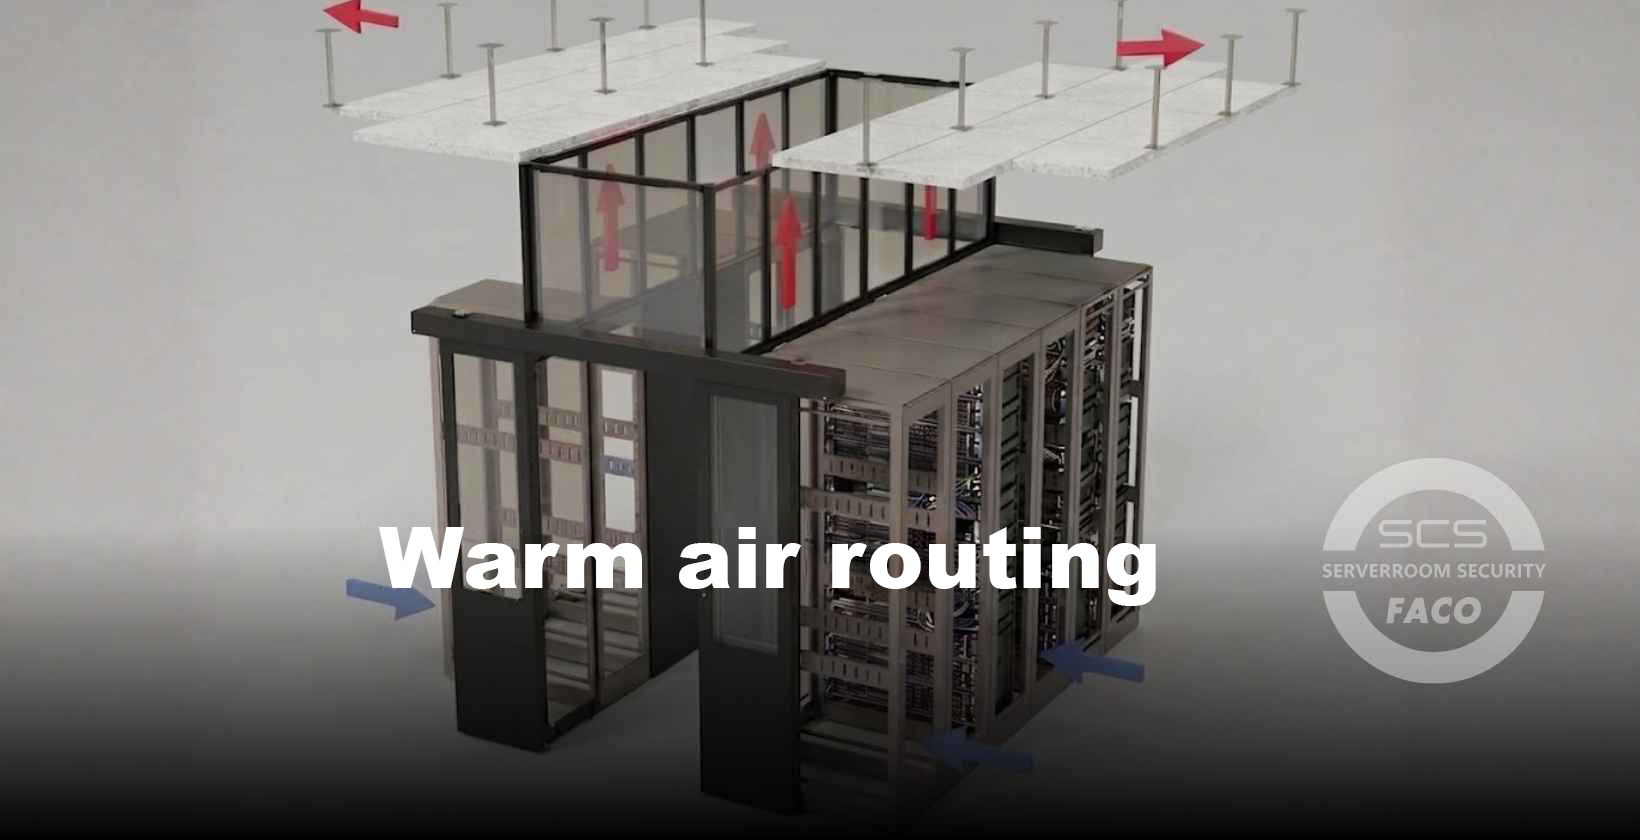
Warm air routing from SCS FACO
Warm air routing is an essential component of data center air conditioning with hot aisle and cold aisle systems. It ensures that the heat generated by servers and other IT components is dissipated in a controlled manner from the immediate rack area.
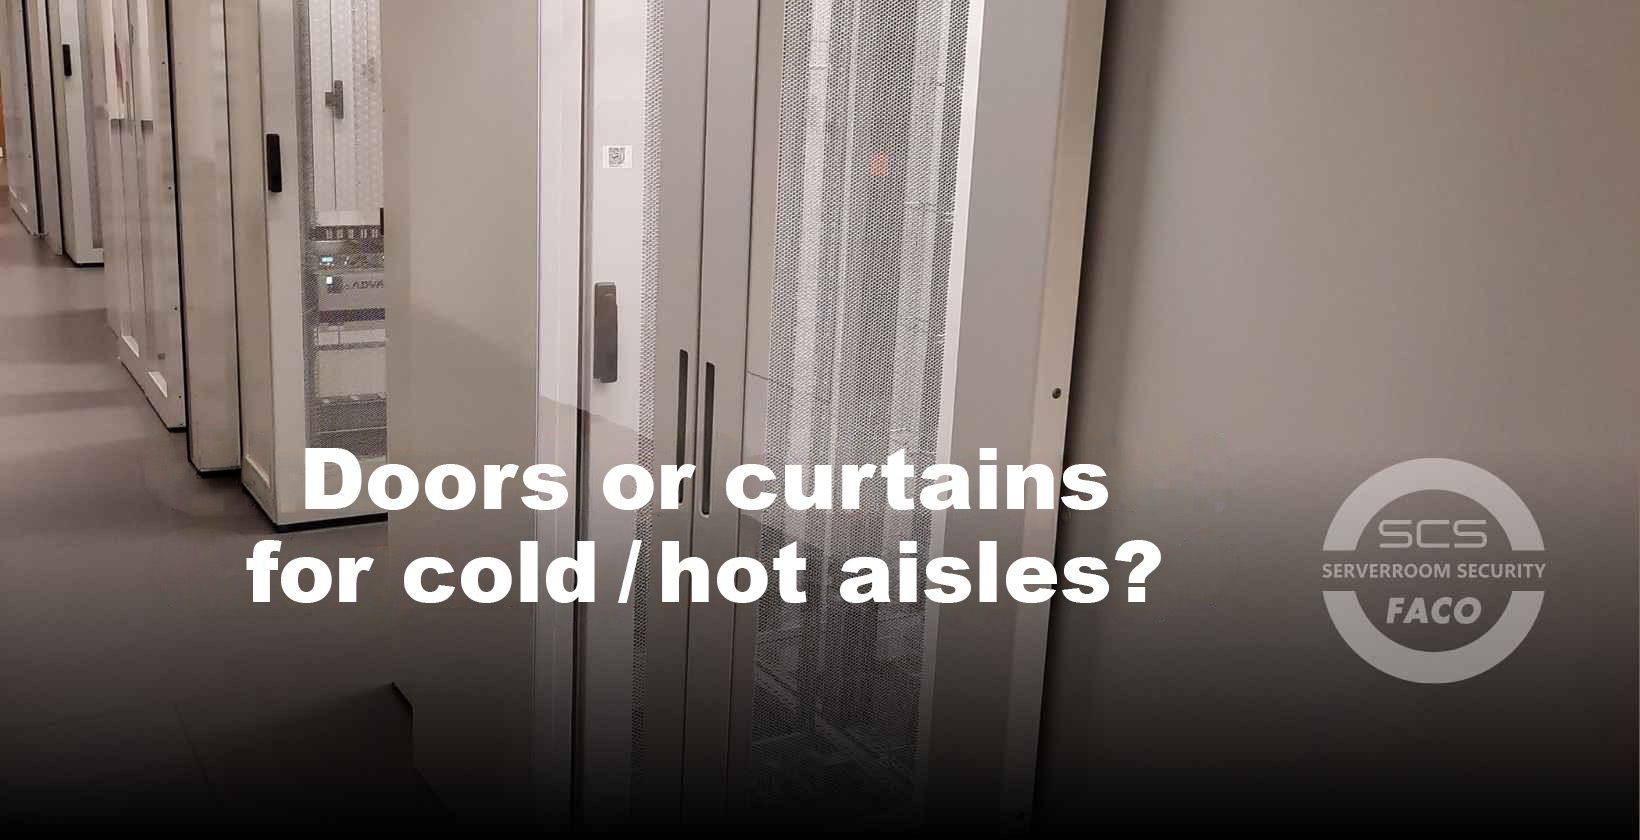
Doors or curtains for cold / hot aisles?
Whether doors or a curtain are more suitable for the cold aisle / hot aisle depends on the individual room conditions and framework within the server room.
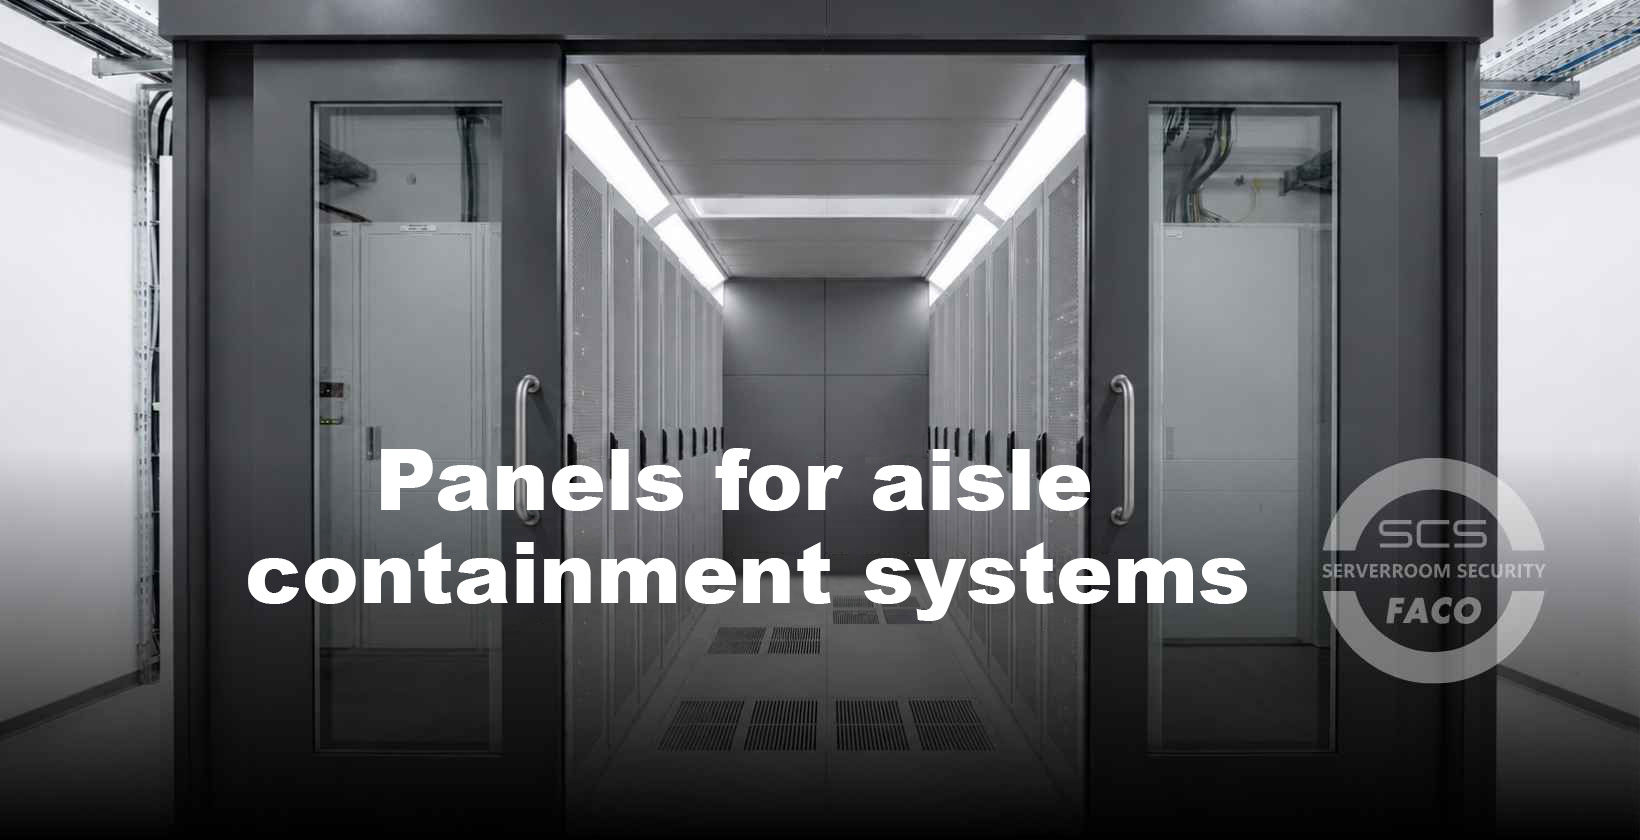
Panels for aisle containment systems from SCS FACO
SCS FACO's aisle containment panels are modular in design and can be individually adapted to existing or planned rack systems.